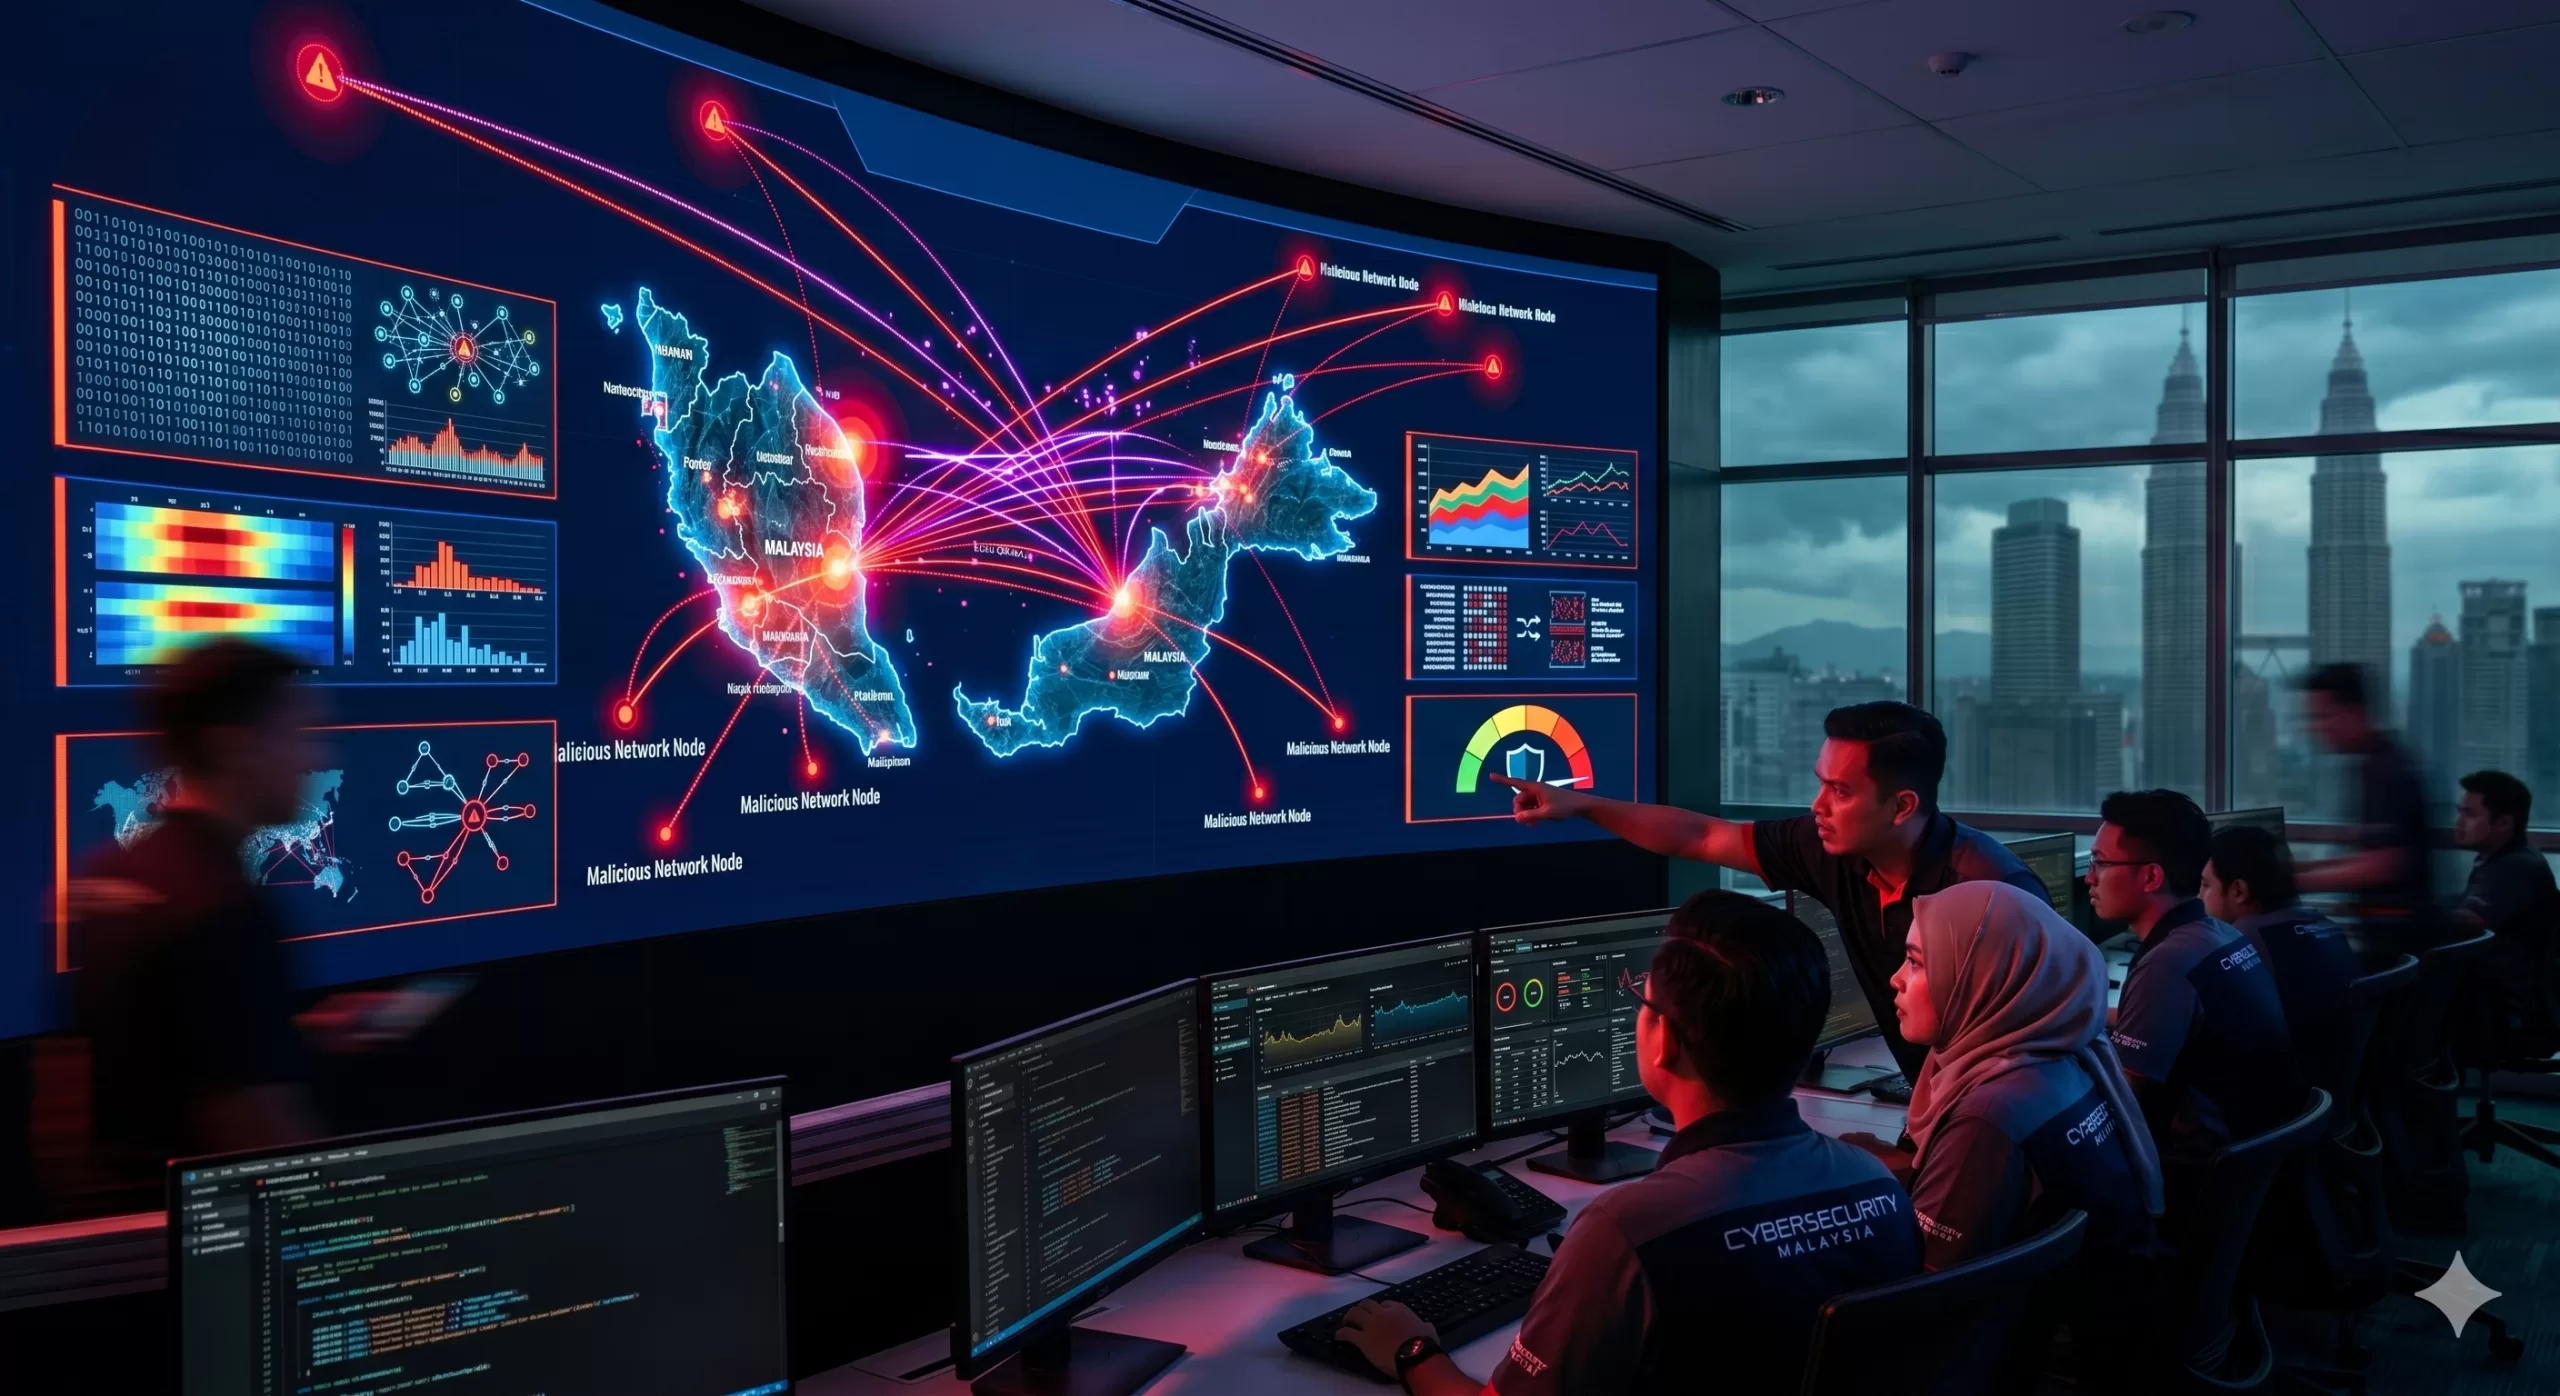
Running a modern business means operating in an inherently connected digital environment, which inevitably invites a constant stream of cyber threats. According to the latest data released by global cybersecurity firm Kaspersky, organisations across Southeast Asia faced a relentless barrage of online attacks last year. In 2025 alone, Kaspersky detected and blocked over 18 million malicious web-based attacks targeting businesses across the region. For Malaysian enterprises, the numbers offer a sobering reality check, as the country registered a staggering 3,361,453 of those web threat incidents.
The Regional Security Landscape
When looking at the broader regional landscape, Malaysia sits as the second most targeted country in Southeast Asia. Vietnam took the top spot by a significant margin with over 8.4 million detected threats, while Indonesia followed closely behind Malaysia with just over 3 million recorded incidents. Meanwhile, organisations in neighbouring Singapore and Thailand also faced intense external pressure, with each country recording over one million web-based cyberattacks throughout the year.
These massive detection figures are a direct reflection of the region’s rapidly expanding digital footprint. The Southeast Asian digital economy is currently valued at approximately US$300 billion and is aggressively tracking towards the US$1 trillion mark by the year 2030. Adrian Hia, Managing Director for Asia Pacific at Kaspersky, pointed out that while the overall quantitative volume of web threats might be experiencing a slight decline in the region, the attacks themselves are evolving as enterprises actively ramp up their internal cybersecurity defences. With technology spending in the Asia Pacific projected to increase by a healthy 9.8% in 2026, businesses are clearly prioritising digital investments to boost their productivity, which inadvertently continues to make them highly lucrative targets for sophisticated cybercriminals.
The Anatomy of a Web Threat
To understand the scale of the risk, it is important to define what a web threat actually entails in a modern corporate setting. These are not just simple, easily identifiable phishing emails. Web threats encompass a wide variety of complex attack vectors, including compromised legitimate websites and malicious background downloads that are specifically engineered to facilitate unauthorised system access or trigger massive corporate data exposures.
The sheer proliferation of smart devices and the widespread adoption of high-speed mobile networks have essentially created an always-connected attack vector. Consequently, the rapid integration of the Internet of Things into everyday corporate communications and productivity tools has significantly outpaced the average employee’s security awareness, creating entirely new, vulnerable entry points for attackers to exploit.
Moving Toward Proactive Defence
Defending against this sheer volume of attacks requires a proactive rather than reactive approach. At a fundamental level, businesses must enforce strict digital hygiene across their entire workforce. This means rigorously keeping operating systems, web browsers, and enterprise applications fully up to date to patch known vulnerabilities before they can be exploited. Furthermore, enforcing strong, unique passwords alongside mandatory two-factor authentication drastically limits the potential operational fallout if employee credentials happen to be compromised.
However, basic digital hygiene is rarely enough for a growing enterprise operating in today’s threat landscape. Kaspersky strongly advises organisations to augment their standard security controls with human-led detection capabilities and global threat intelligence. This involves deploying comprehensive, expert-led solutions like Managed Detection and Response services or utilising highly automated systems like the Kaspersky Next XDR Expert. By seamlessly aggregating data from multiple network sources and applying advanced machine learning to detect anomalies, businesses can establish effective threat detection and rapid automated responses, ensuring their critical data assets remain secure.