This article is written based on an interview with Santanu Dutt, VP and Head of Technology for the APJ region at Zscaler
Let’s be honest about what is happening in corporate offices right now. Artificial intelligence (AI) has exploded onto the scene, and everyone from the front desk to the C-suite is trying to figure out how to squeeze more hours out of the day. For the everyday worker, AI isn’t some abstract sci-fi concept or a boardroom buzzword. It’s a handy tool that drafts emails, summarises messy meeting notes, and untangles complicated spreadsheets in seconds.
When management responds to this sudden wave of adoption with blanket bans and corporate roadblocks, they are missing the forest for the trees. Stubborn resistance is not a sustainable strategy, and pretending that employees won’t use AI is a fast track to irrelevance.
To understand why traditional bans fail so spectacularly, we have to look at the daily realities of the modern workplace.
Why Everyday Workers Reach for Unvetted AI
Let’s put ourselves in the shoes of an everyday professional. You have a mountain of reports to process, a tight deadline looming, and a boss asking for a comprehensive market analysis before lunch. You open your corporate laptop, only to find that your IT department has locked down or completely blocked access to popular consumer AI tools.
Does that stop you? Absolutely not.
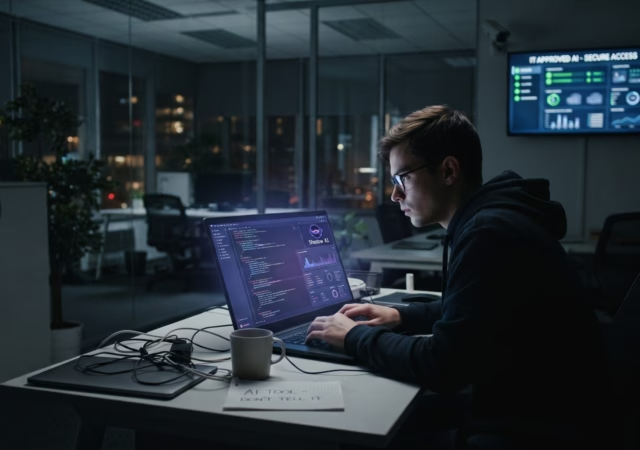
When employees are blocked from using efficient tools, they don’t simply give up and work slower. They find a workaround. As Santanu Dutt, Vice President and Head of Technology for APJ at Zscaler, points out, human ingenuity always finds a bypass when faced with productivity bottlenecks:
“If you block an application, a motivated employee will use their personal mobile phone to photograph internal documents and feed that data into a consumer AI tool. The data has effectively left the building anyway, just through a channel you cannot see.”
Think about that for a second. That is the fundamental flaw of a heavy-handed ban. By trying to protect sensitive corporate data through prohibition, companies inadvertently create an invisible, unmonitored blind spot. The data leaves the building anyway, captured on a personal smartphone screen, pasted into an unvetted public chatbot, and processed on servers halfway across the world. The corporate network perimeter didn’t hold; it was bypassed by a simple handheld camera.
This is what we call Shadow AI. And it is quietly turning into one of the most dangerous data governance crises facing modern enterprises today.
The Mirage of Total Control
For IT departments and C-level executives, the knee-jerk reaction to security risks has always been control through restriction. If a tool looks risky, lock it down. If an application isn’t officially sanctioned, add it to the firewall blacklist.
Unfortunately, the data tells a sobering story about how well that strategy is working. Zscaler’s ThreatLabz data highlights that AI adoption surged by a staggering 91% year-over-year. Meanwhile, a vast number of organisations still cannot produce a basic inventory of the AI tools actively running inside their own environments.
The issue is no longer about whether employees are using AI. They are using it because it genuinely makes them faster, sharper, and more efficient. The real problem is that without sanctioned, secure alternatives provided by the company, workers reach for whatever is available on the open web.
When convenience trumps compliance every single time, blocking everything AI becomes a losing battle. As Dutt bluntly notes, that war is already lost:
“The goal is not to block everything AI. That battle is already lost.”
So, if blocking doesn’t work and ignoring the problem invites a catastrophic data leak, what is the realistic middle ground? How do enterprises cater to everyday Joes who just want to get their work done while assuring executives that proprietary secrets aren’t leaking onto public servers?
Finding the Realistic Middle Ground
Building a secure AI environment doesn’t mean locking the front door and throwing away the key. It requires a fundamental shift in how organisations approach network visibility and data protection. According to tech industry leaders like Zscaler, a sustainable strategy rests on three core pillars working in tandem.
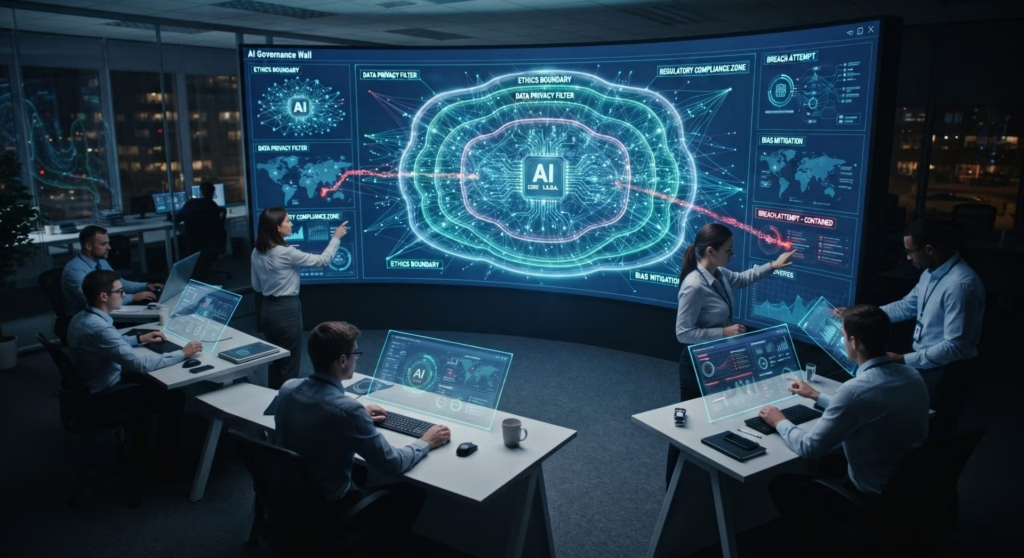
First, companies need total visibility into every single AI transaction happening across their network. You cannot govern what you cannot see. If shadow AI tools are operating in the background, IT teams need real-time mapping to identify them instantly, whether they are standalone web apps or hidden features baked into existing software suites.
Second, organisations must enforce specific AI guardrails. This ensures that sanctioned tools behave precisely as intended. For example, a customer support chatbot used by everyday employees should be strictly blocked from spitting out internal legal advice or answering complex code questions it was never trained to handle. Hardening these guardrails protects against prompt injection and jailbreak manipulation before sensitive data ever touches an external model.
Finally, companies need out-of-the-box controls that govern what an automated agent can and cannot do.
When these three elements work together, the presence of shadow AI changes from an existential threat into a managed variable. As Dutt explains:
“The realistic middle ground requires three things working together: full visibility into every AI transaction happening across the organisation; enforcement of specific AI guardrails so that sanctioned tools behave as intended; and the ability to apply out-of-the-box controls that govern what an agent can and cannot do.”
With these guardrails and visibility tools active, the exact number of shadow AI applications floating around your network suddenly matters a lot less. You can see them all, understand how they interact with your data, and respond at machine speed without placing frustrating roadblocks in front of your workforce.
Bridging the Gap for C-Suites and Everyday Joes
At the end of the day, bridging the gap between C-suite security demands and everyday productivity comes down to empathy and smart architecture.
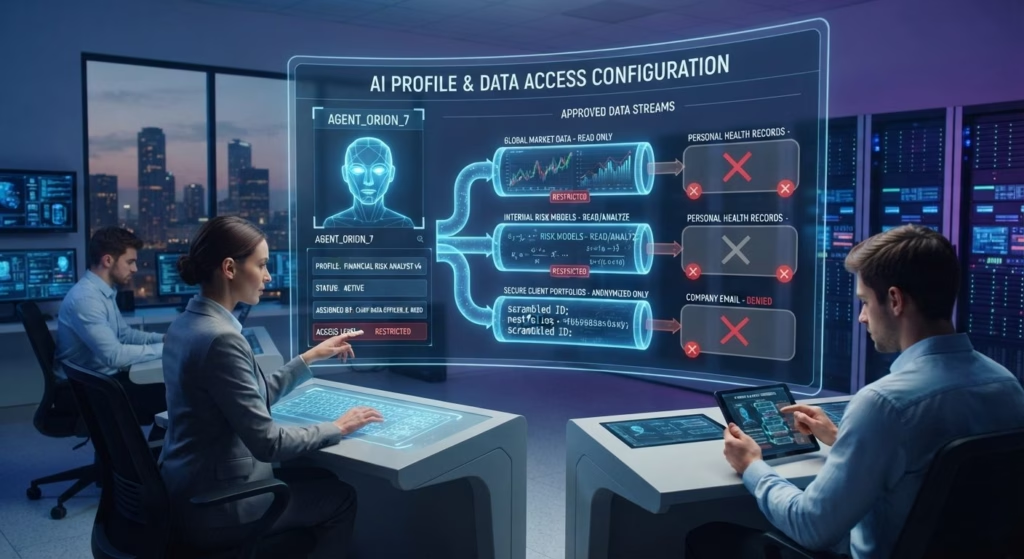
Executives are right to worry about data sovereignty, regulatory compliance under frameworks like Malaysia’s Cyber Security Act 2024, and the expanding blast radius of human error. A single unclassified document left in a public folder can spiral into global headlines. But punishing employees for trying to be productive is not the answer.
Instead of waging a futile war against human efficiency, organisations must shift their focus toward data-first defence. By automating data classification so sensitive files are tagged and restricted by default, and by utilising inline Data Loss Prevention (DLP) to intercept risky prompts in real time, companies can protect their assets without slowing down their people.
Policies must apply to the data itself, not to the human beings moving it. When technology steps in to catch mistakes before they happen, everyday workers get the freedom to innovate, C-suites get the ironclad security they require, and techENT readers get the best of both worlds.
This article is written based on an interview with Santanu Dutt, VP and Head of Technology for the APJ region at Zscaler
Santanu Dutt
VP and Head of Technology, Zscaler
Santanu Dutt is the Vice President and Head of Technology for the Asia-Pacific and Japan region at Zscaler, having assumed the role in July 2025. With years of experience in the IT sector, Santanu previously held various positions at Amazon Web Services (AWS), including Head of Technology / CTO and Head of Customer Solutions Management for Asia-Pacific and Japan, as well as managing Solutions Architect Teams in Southeast Asia. Santanu’s earlier experience also includes roles in Solutions Architecture with Red Hat and system administration at Accenture IDC. He has a Bachelor of Engineering in Electronics from R.A.I.T.